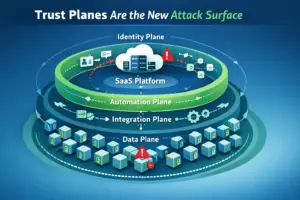
“Trust Planes” Are the New Attack Surface
Attackers are no longer “breaking in.” They are logging in—through stolen sessions, abused automations, and over-scoped integrations that your systems were designed to trust. Trust planes are the new attack surface. This post maps the planes, the kill chain, and the controls that matter—then shows why data-plane containment is the only durable way to prevent wholesale compromise.
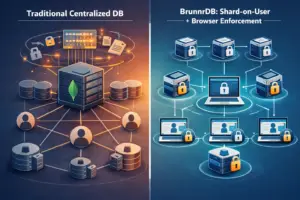
Preventing Cross‑Tenant Breaches: How BrunnrDB’s Architecture Contains Attacks Post‑MongoBleed
MongoBleed (CVE-2025-14847) showed how one flaw in a centralized database leaks data across tenants. How per-user sharding and client-side encryption contain the damage.
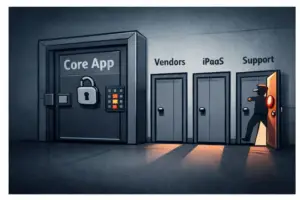
Vendor Breach Containment: Making Integrations Safe Even When They Get Popped
Vendor breaches are no longer an edge case—they are a primary way attackers bypass your “front door” controls. A single compromised integration can turn into wholesale data access if it relies on long-lived tokens, broad permissions, unmanaged exports, or direct database connectivity. This post turns the “side doors” risk into an actionable containment checklist: minimize what vendors can reach, shorten how long access works, and reduce the value
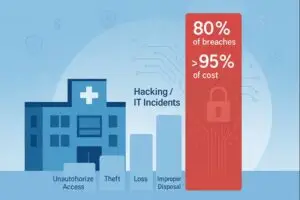
When Healthcare Breaches Happen, Cyber Attacks Pay the Highest Price: Insights from Two Years of HHS OCR Data
Over the last two years, large healthcare data breaches reported to the U.S. Department of Health and Human Services (HHS) Office for Civil Rights (OCR) have revealed a consistent pattern: almost all of the risk and almost all of the cost sit in one place – server aggregated data.
Sharding to Contain the Blast Radius of Data Breaches
Modern SaaS platforms sit on top of massive, multi-tenant data stores. When those stores are breached, the damage is rarely limited to a single record; it is often “wholesale” compromise of large slices of the user base. For a CISO or CTO, this is the critical risk: not that a record can be stolen, but that everything a given system knows becomes available in one incident.
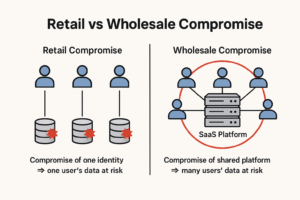
When SaaS Fails, It Fails at Scale: Why Data-in-Use Protection Matters
One flaw in a shared SaaS platform can expose millions of users at once. Why wholesale compromise is structural, and how data-in-use protection with sharding contains it.