“Trust Planes” Are the New Attack Surface
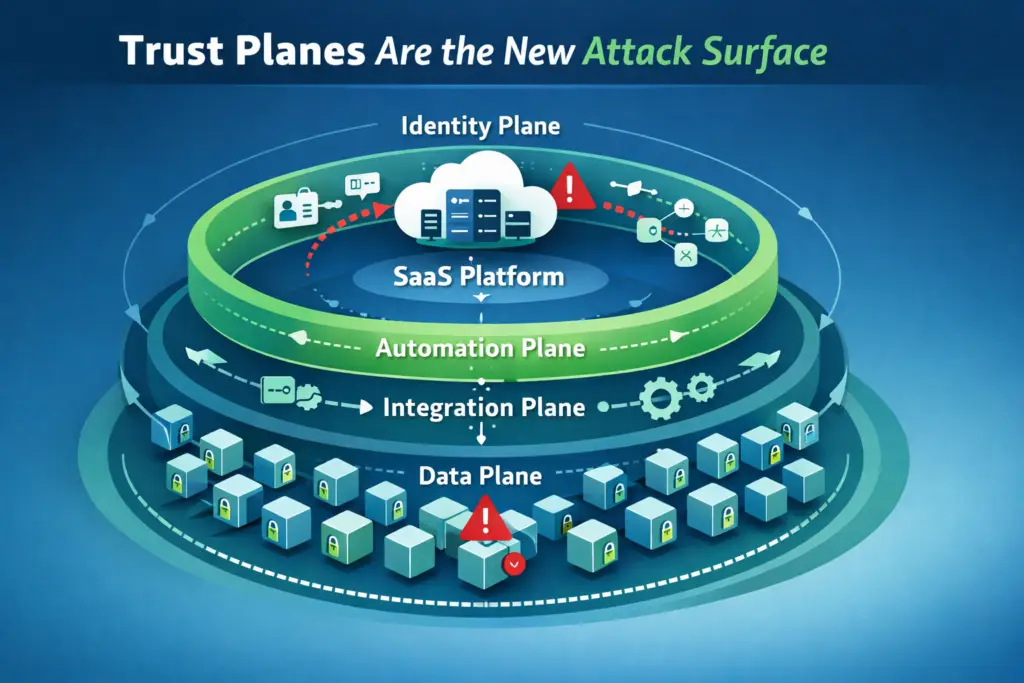
Attackers are no longer “breaking in.” They are logging in—through stolen sessions, abused automations, and over-scoped integrations that your systems were designed to trust. Trust planes are the new attack surface. This post maps the planes, the kill chain, and the controls that matter—then shows why data-plane containment is the only durable way to prevent wholesale compromise.
Vendor Breach Containment: Making Integrations Safe Even When They Get Popped
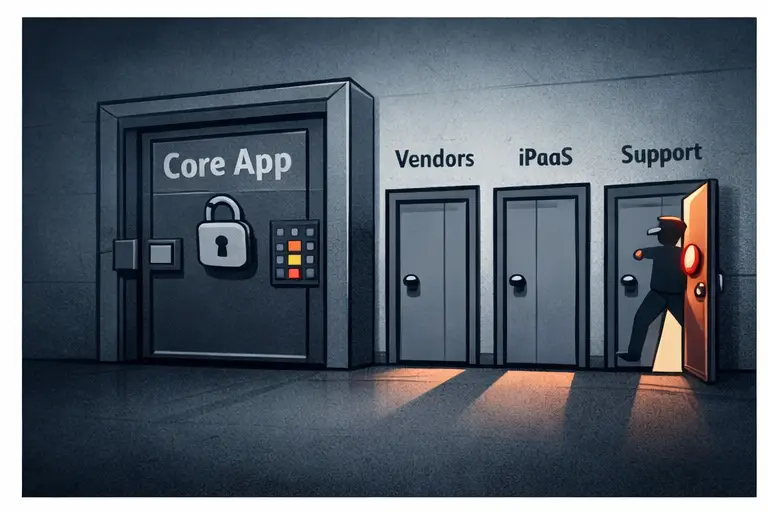
Vendor breaches are no longer an edge case—they are a primary way attackers bypass your “front door” controls. A single compromised integration can turn into wholesale data access if it relies on long-lived tokens, broad permissions, unmanaged exports, or direct database connectivity. This post turns the “side doors” risk into an actionable containment checklist: minimize what vendors can reach, shorten how long access works, and reduce the value of anything that leaks. You will find practical patterns—an integration gateway, curated exports, kill switches, and tight token scopes—that make stolen vendor access boring and keep blast radius small.
The Hidden Risk in Cloud Databases: When a Vendor Breach Becomes Your Breach
Most companies lock down their apps – but leave the side doors wide open.
Those “side doors” are your vendors, integrations, and managed services.