The Server Will Be Compromised. What Can It Surrender?
The first reported breach carried out by an AI agent shows attacks moving at machine speed. The real question: what can a compromised server surrender?
“Trust Planes” Are the New Attack Surface
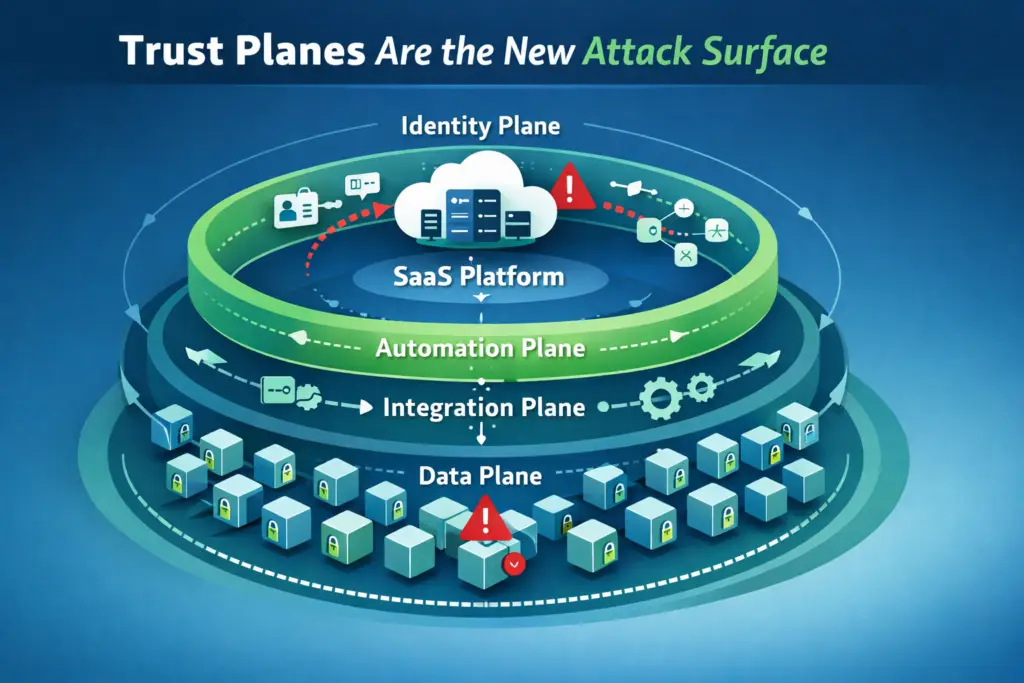
Attackers are no longer “breaking in.” They are logging in—through stolen sessions, abused automations, and over-scoped integrations that your systems were designed to trust. Trust planes are the new attack surface. This post maps the planes, the kill chain, and the controls that matter—then shows why data-plane containment is the only durable way to prevent wholesale compromise.
Vendor Breach Containment: Making Integrations Safe Even When They Get Popped
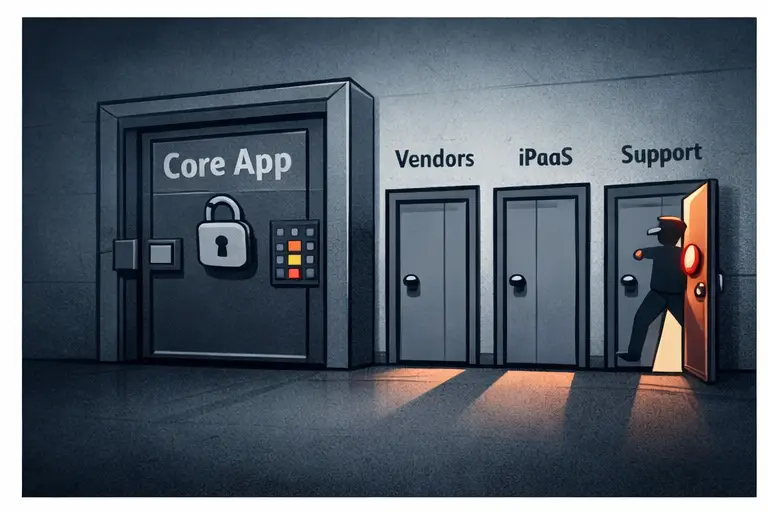
Vendor breaches are no longer an edge case—they are a primary way attackers bypass your “front door” controls. A single compromised integration can turn into wholesale data access if it relies on long-lived tokens, broad permissions, unmanaged exports, or direct database connectivity. This post turns the “side doors” risk into an actionable containment checklist: minimize what vendors can reach, shorten how long access works, and reduce the value of anything that leaks. You will find practical patterns—an integration gateway, curated exports, kill switches, and tight token scopes—that make stolen vendor access boring and keep blast radius small.
Sharding to Contain the Blast Radius of Data Breaches

Modern SaaS platforms sit on top of massive, multi-tenant data stores. When those stores are breached, the damage is rarely limited to a single record; it is often “wholesale” compromise of large slices of the user base. For a CISO or CTO, this is the critical risk: not that a record can be stolen, but that everything a given system knows becomes available in one incident.
When SaaS Fails, It Fails at Scale: Why Data-in-Use Protection Matters
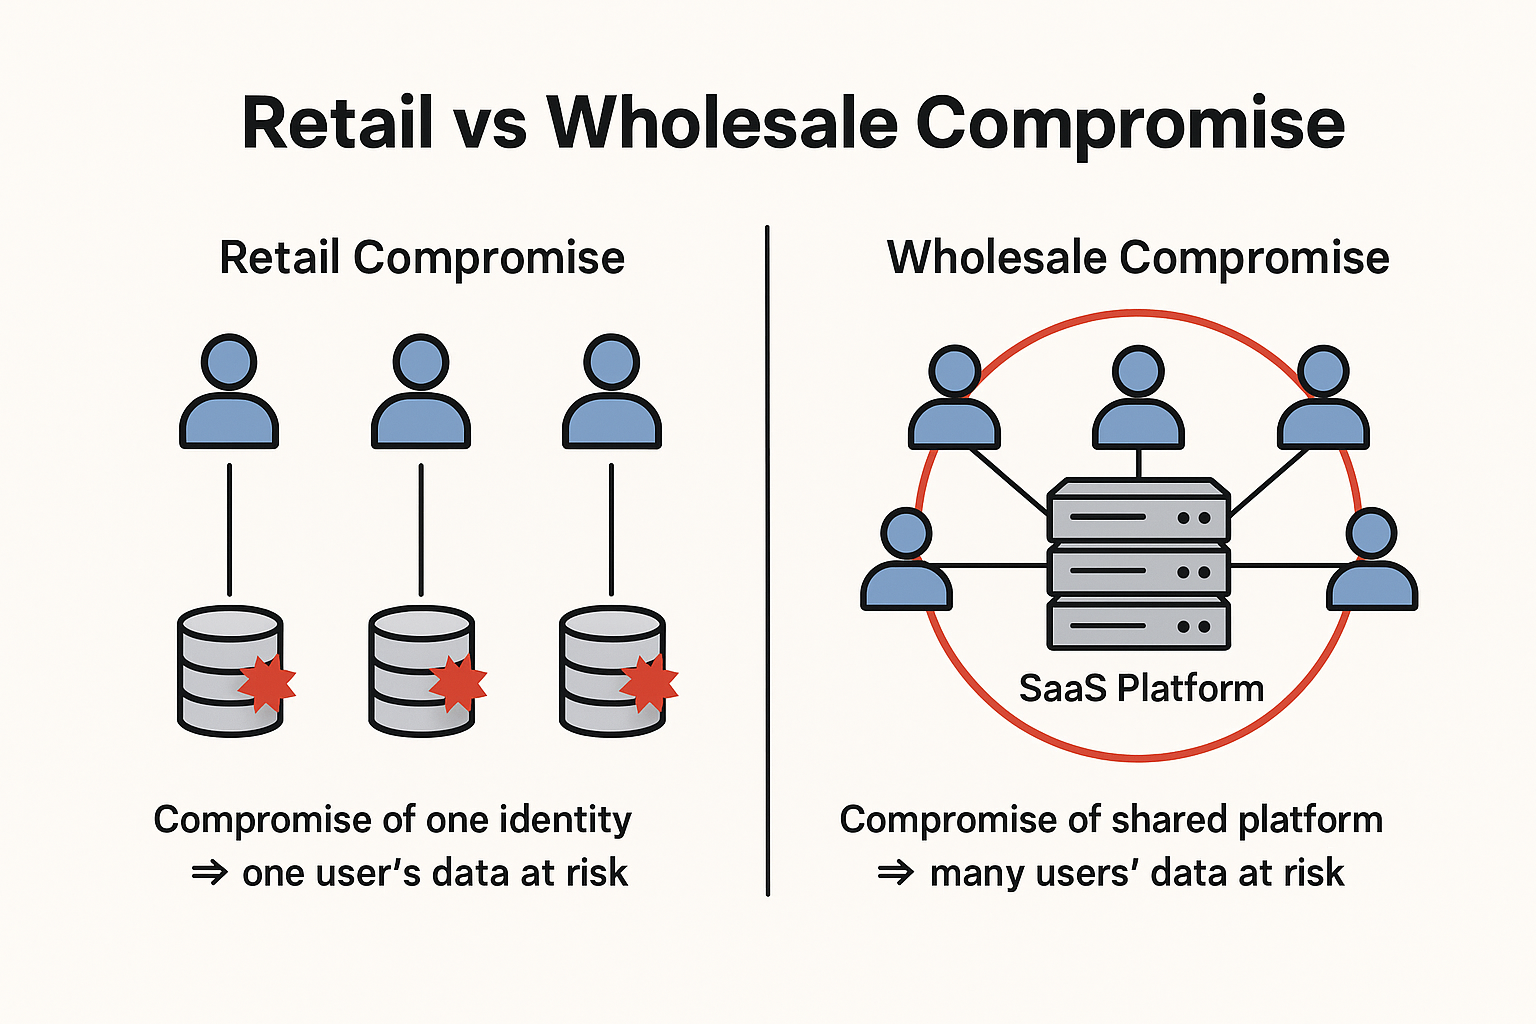
One flaw in a shared SaaS platform can expose millions of users at once. Why wholesale compromise is structural, and how data-in-use protection with sharding contains it.