A Valid Login Is Not the Same as Legitimate Access
A valid login is not legitimate access. Change Healthcare, PowerSchool and Salesforce show how compromised authority becomes mass data exposure.
Preventing Cross‑Tenant Breaches: How BrunnrDB’s Architecture Contains Attacks Post‑MongoBleed
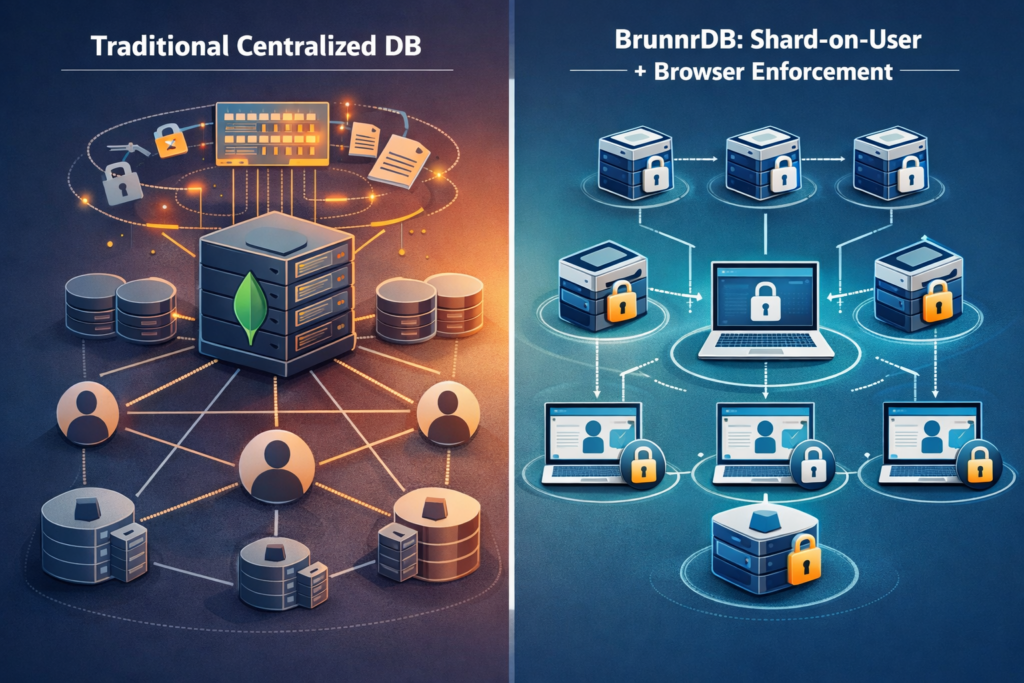
MongoBleed (CVE-2025-14847) showed how one flaw in a centralized database leaks data across tenants. How per-user sharding and client-side encryption contain the damage.
Sharding to Contain the Blast Radius of Data Breaches

Modern SaaS platforms sit on top of massive, multi-tenant data stores. When those stores are breached, the damage is rarely limited to a single record; it is often “wholesale” compromise of large slices of the user base. For a CISO or CTO, this is the critical risk: not that a record can be stolen, but that everything a given system knows becomes available in one incident.
When SaaS Fails, It Fails at Scale: Why Data-in-Use Protection Matters
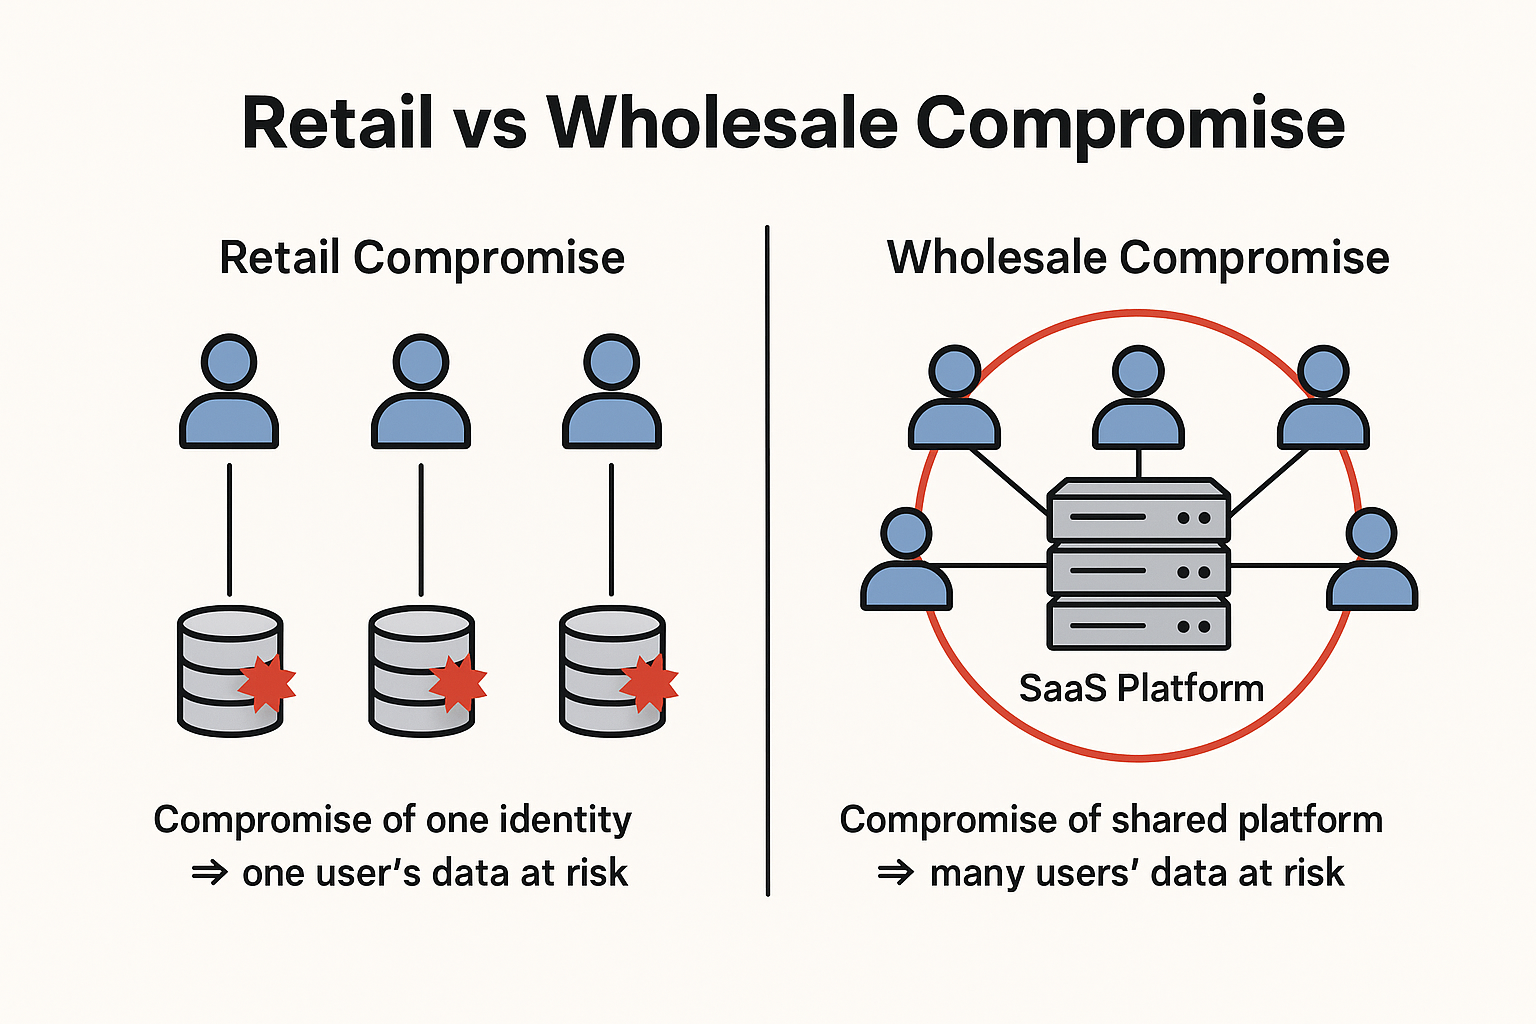
One flaw in a shared SaaS platform can expose millions of users at once. Why wholesale compromise is structural, and how data-in-use protection with sharding contains it.