Preventing Cross‑Tenant Breaches: How BrunnrDB’s Architecture Contains Attacks Post‑MongoBleed
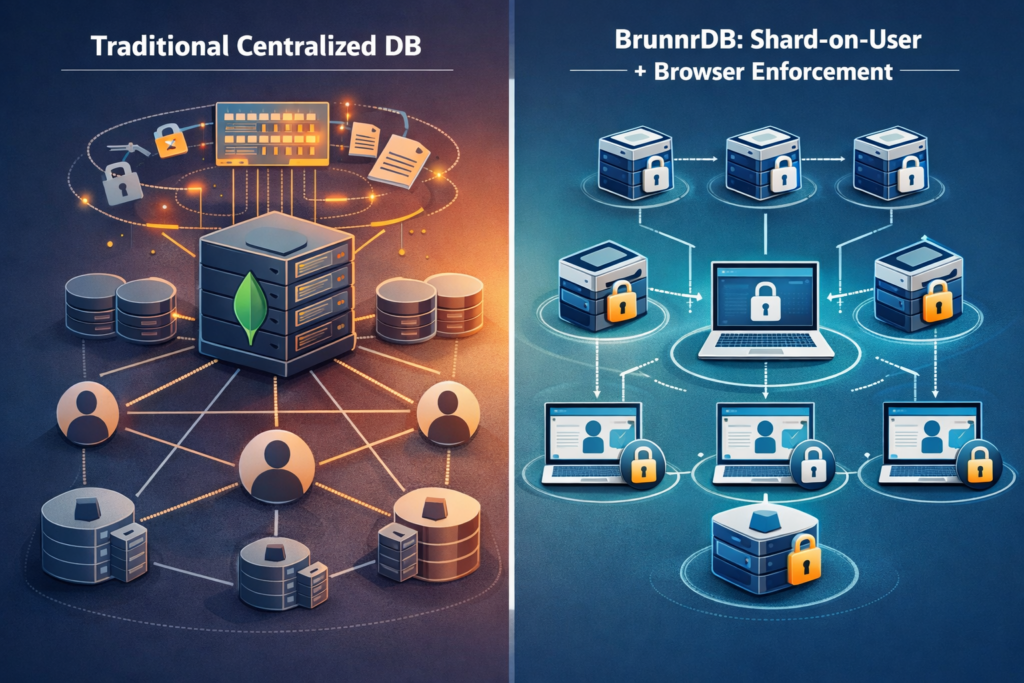
MongoBleed (CVE-2025-14847) showed how one flaw in a centralized database leaks data across tenants. How per-user sharding and client-side encryption contain the damage.
When SaaS Fails, It Fails at Scale: Why Data-in-Use Protection Matters
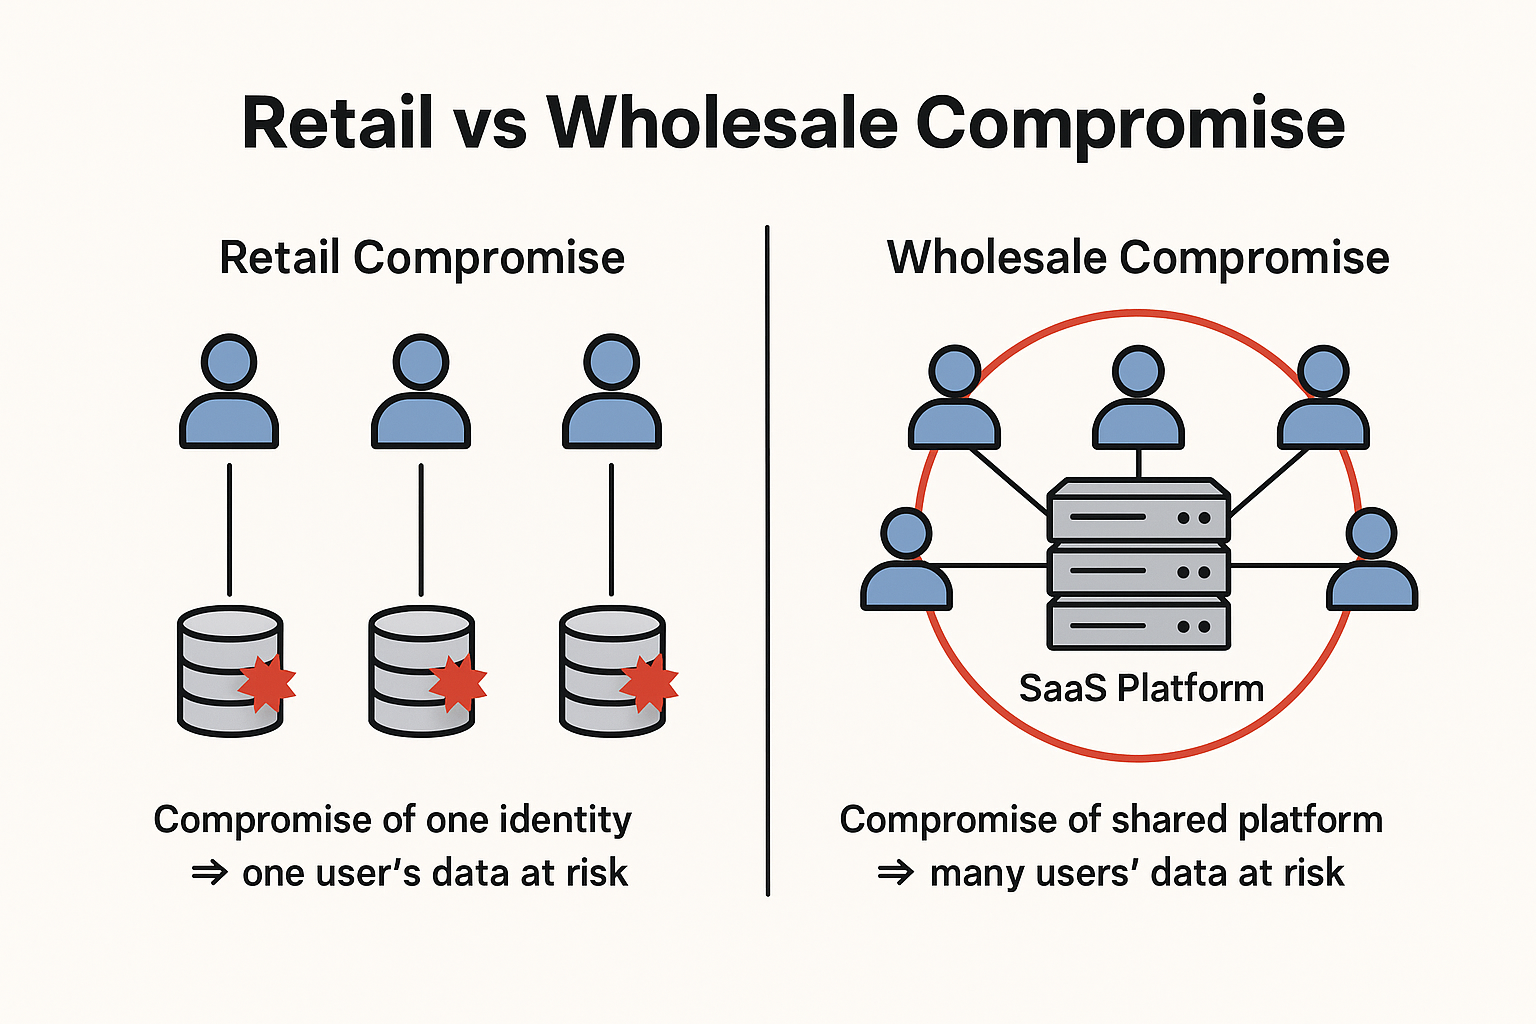
One flaw in a shared SaaS platform can expose millions of users at once. Why wholesale compromise is structural, and how data-in-use protection with sharding contains it.
Protecting Data-In-Use in the Cloud: A Pragmatic Philosophy
Once an attacker can read memory, encryption at rest and MFA stop helping. A pragmatic approach to data-in-use: trust the session, not the environment, and assume breach.
The Lifecycle of a Hacked Database – and Why Aggregated Data Takes the Biggest Hit
A database breach isn’t a single event—it’s a story that unfolds in stages.
Each stage brings attackers closer to the crown jewels: your aggregated data.
Closing the Encryption Gap: Protecting Data While It’s Being Used
Encryption protects data at rest and in transit – but what about when it’s being used?
That’s the missing layer in most security architectures.