When SaaS Fails, It Fails at Scale: Why Data-in-Use Protection Matters
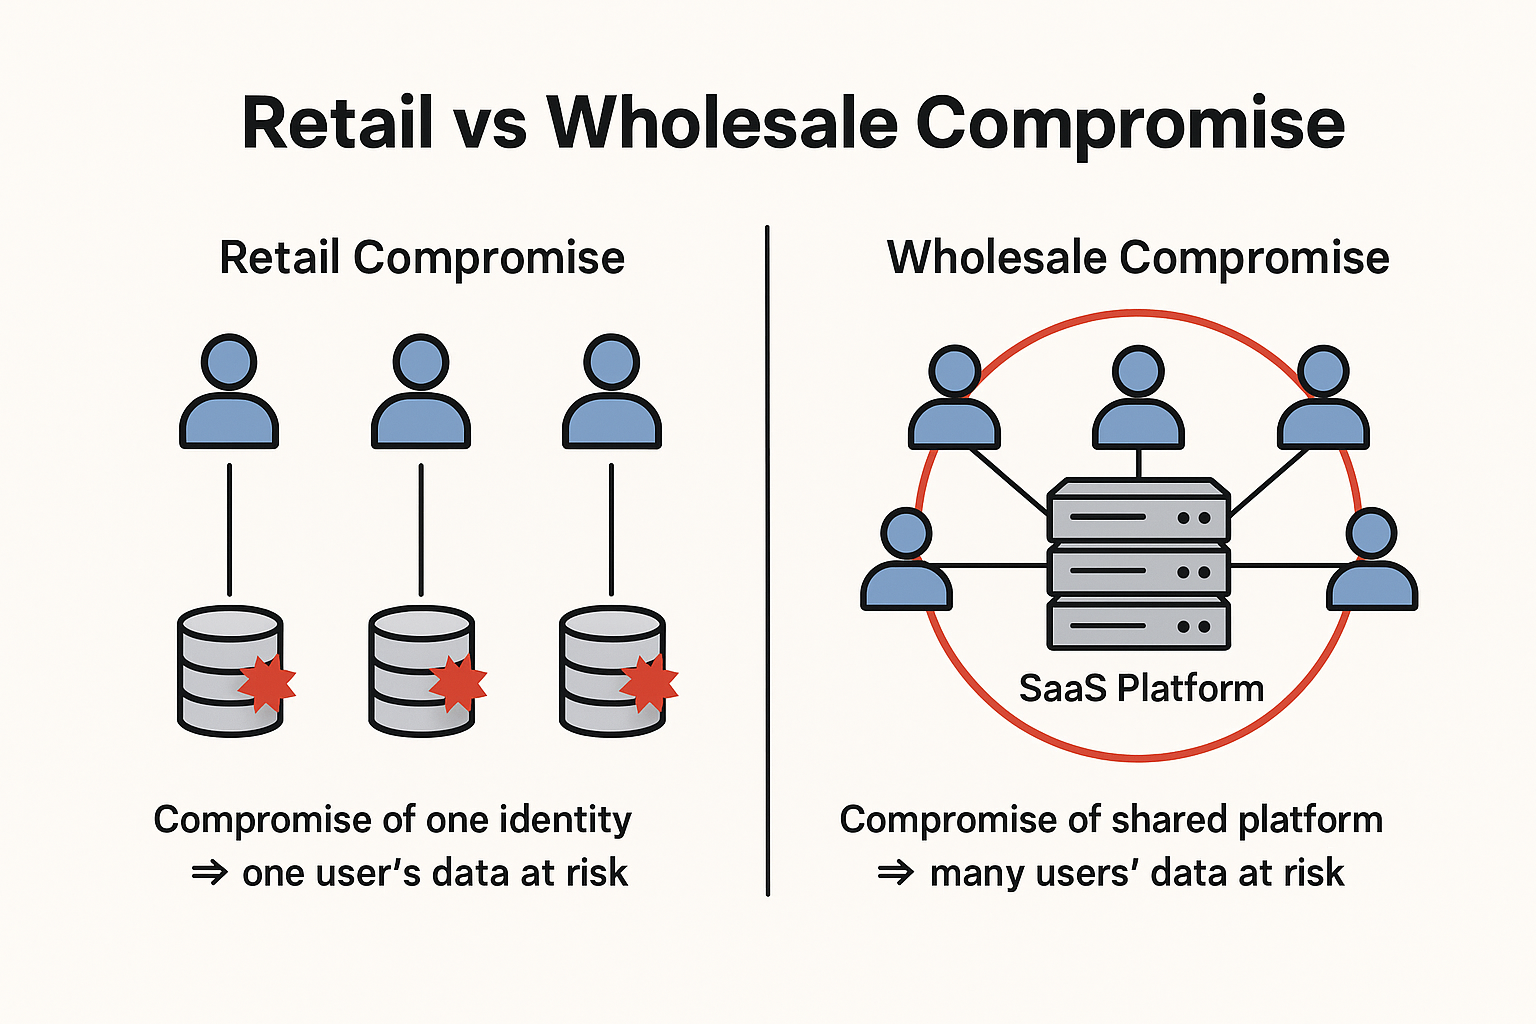
One flaw in a shared SaaS platform can expose millions of users at once. Why wholesale compromise is structural, and how data-in-use protection with sharding contains it.
Protecting Data-In-Use in the Cloud: A Pragmatic Philosophy
Once an attacker can read memory, encryption at rest and MFA stop helping. A pragmatic approach to data-in-use: trust the session, not the environment, and assume breach.
The Hidden Risk in Cloud Databases: When a Vendor Breach Becomes Your Breach
Most companies lock down their apps – but leave the side doors wide open.
Those “side doors” are your vendors, integrations, and managed services.
Closing the Encryption Gap: Protecting Data While It’s Being Used
Encryption protects data at rest and in transit – but what about when it’s being used?
That’s the missing layer in most security architectures.