The Server Will Be Compromised. What Can It Surrender?
The first reported breach carried out by an AI agent shows attacks moving at machine speed. The real question: what can a compromised server surrender?
“Trust Planes” Are the New Attack Surface
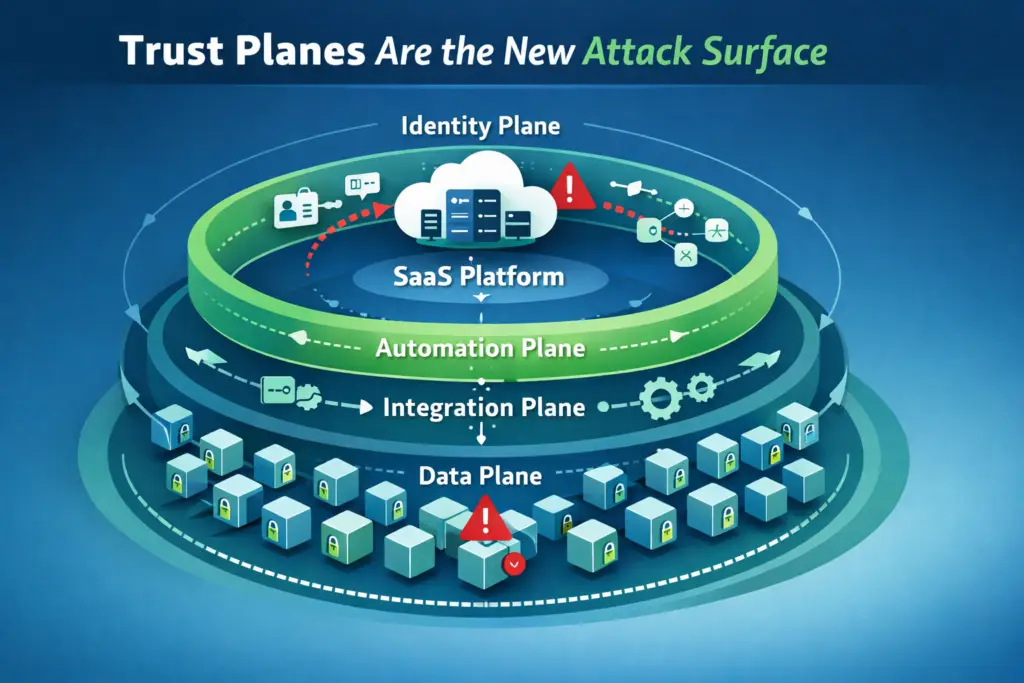
Attackers are no longer “breaking in.” They are logging in—through stolen sessions, abused automations, and over-scoped integrations that your systems were designed to trust. Trust planes are the new attack surface. This post maps the planes, the kill chain, and the controls that matter—then shows why data-plane containment is the only durable way to prevent wholesale compromise.
Preventing Cross‑Tenant Breaches: How BrunnrDB’s Architecture Contains Attacks Post‑MongoBleed
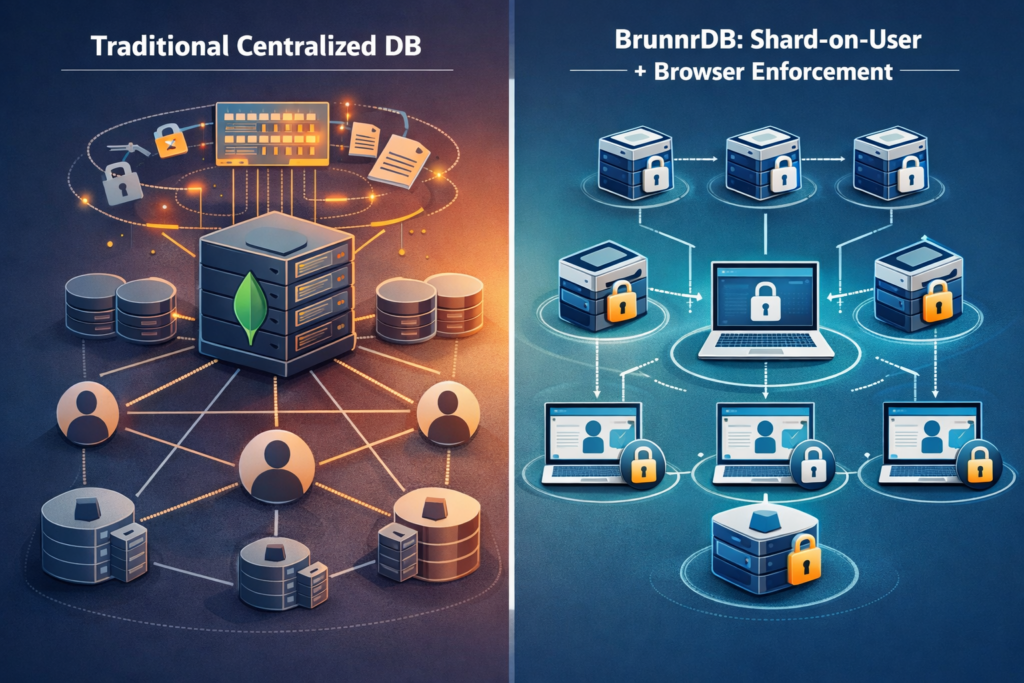
MongoBleed (CVE-2025-14847) showed how one flaw in a centralized database leaks data across tenants. How per-user sharding and client-side encryption contain the damage.
Vendor Breach Containment: Making Integrations Safe Even When They Get Popped
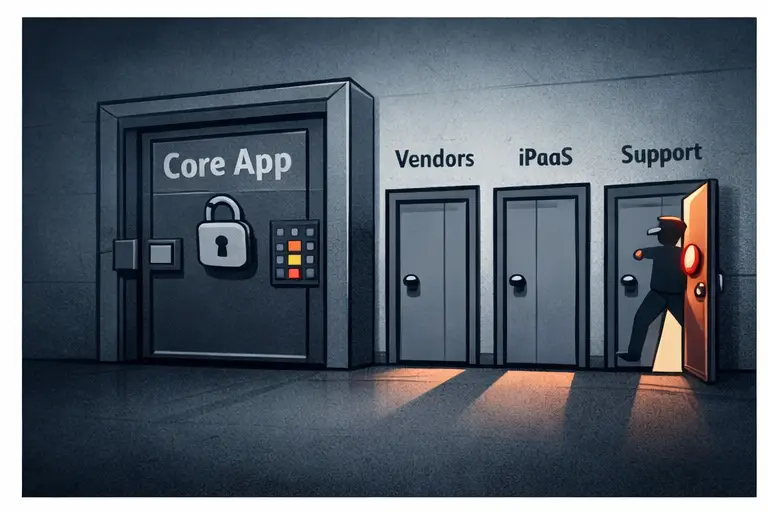
Vendor breaches are no longer an edge case—they are a primary way attackers bypass your “front door” controls. A single compromised integration can turn into wholesale data access if it relies on long-lived tokens, broad permissions, unmanaged exports, or direct database connectivity. This post turns the “side doors” risk into an actionable containment checklist: minimize what vendors can reach, shorten how long access works, and reduce the value of anything that leaks. You will find practical patterns—an integration gateway, curated exports, kill switches, and tight token scopes—that make stolen vendor access boring and keep blast radius small.
Sharding to Contain the Blast Radius of Data Breaches

Modern SaaS platforms sit on top of massive, multi-tenant data stores. When those stores are breached, the damage is rarely limited to a single record; it is often “wholesale” compromise of large slices of the user base. For a CISO or CTO, this is the critical risk: not that a record can be stolen, but that everything a given system knows becomes available in one incident.
The Hidden Risk in Cloud Databases: When a Vendor Breach Becomes Your Breach
Most companies lock down their apps – but leave the side doors wide open.
Those “side doors” are your vendors, integrations, and managed services.
The Lifecycle of a Hacked Database – and Why Aggregated Data Takes the Biggest Hit
A database breach isn’t a single event—it’s a story that unfolds in stages.
Each stage brings attackers closer to the crown jewels: your aggregated data.
Closing the Encryption Gap: Protecting Data While It’s Being Used
Encryption protects data at rest and in transit – but what about when it’s being used?
That’s the missing layer in most security architectures.